A batch of unpatched Linux kernel vulnerabilities ended up on a public mailing list by mistake this week, and some of the flaws score as high as 9 out of 10 on the CVSS scale, the industry's standard measure of how dangerous a security bug is.
Phoronix's Michael Larabel first flagged the mix-up, reporting that the vulnerability reports appear to have originated from Trend Micro's Zero Day Initiative, a program that pays outside researchers to find and report bugs responsibly rather than dump them online. Instead of going to the kernel's private security list, where maintainers quietly work on fixes before details go public, the reports landed somewhere anyone could read them.
That's a problem because none of the flaws had been patched in the mainline kernel at the time the list leaked. The attack details are now out there, and the fixes aren't, at least not yet on the stable branch most people run.
Greg Kroah-Hartman, who maintains the Linux kernel's stable branch and is effectively the kernel's second-in-command behind Linus Torvalds, responded to each report individually, according to Phoronix, asking the submitters to correct how they're filing these in the future. He didn't rush out emergency patches on the spot, but some of the flagged issues are reportedly already in testing or queued for upcoming beta and '-next' branches, which is where kernel changes get tried out before they're considered stable enough for everyone.
What this means for SteamOS and other Linux distros
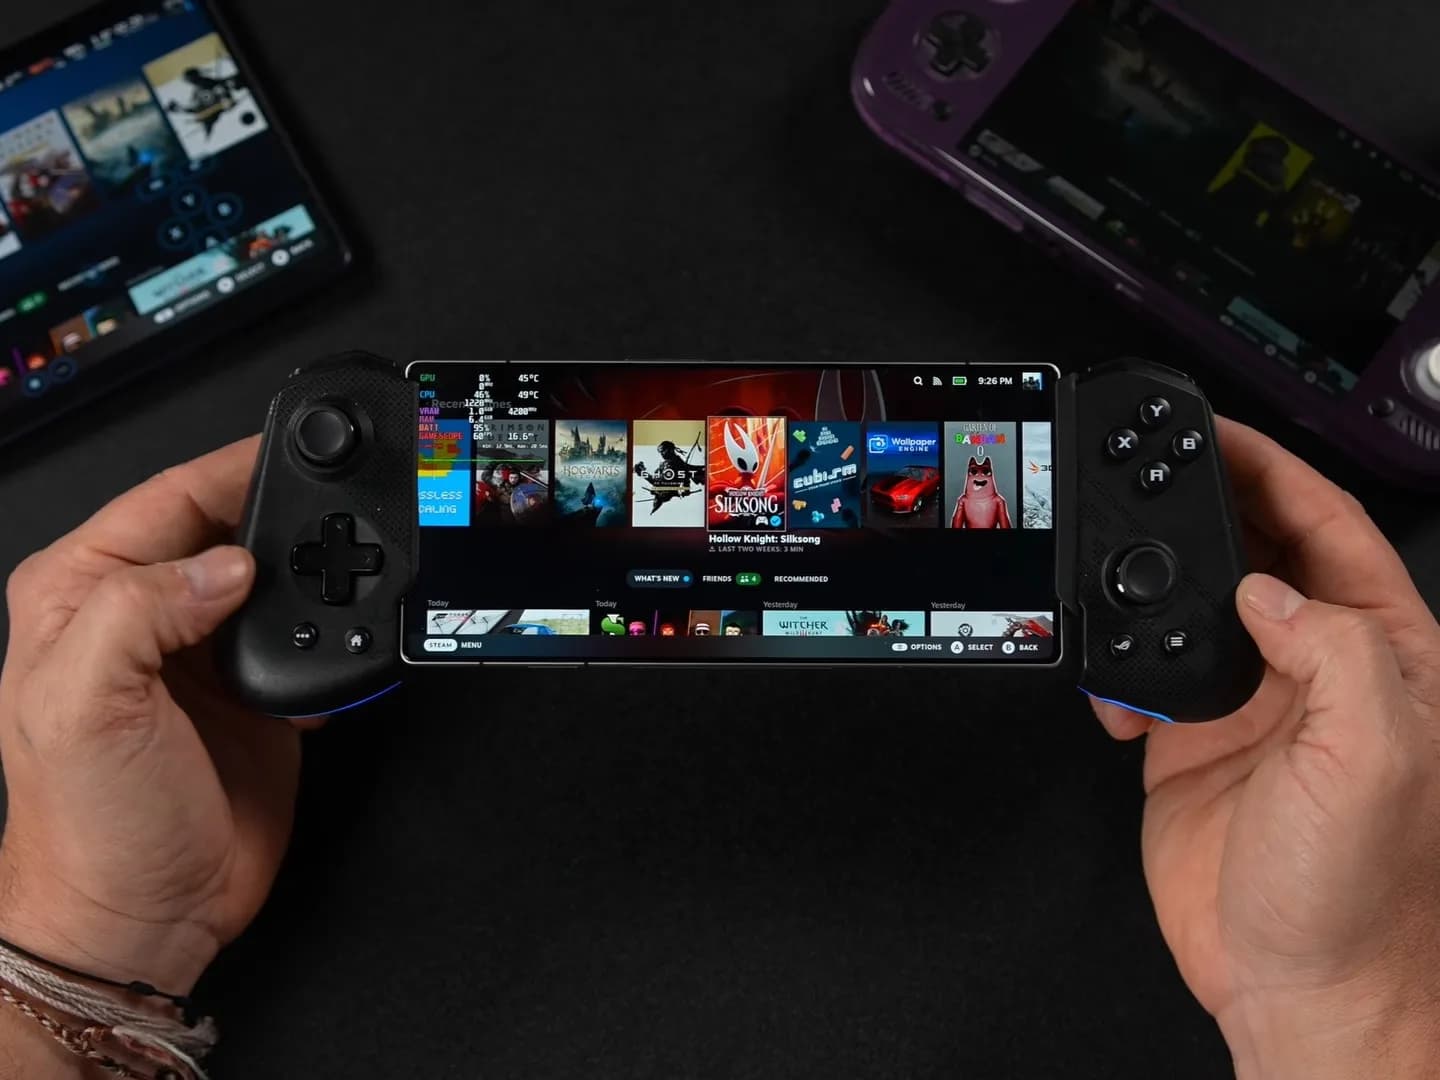
This matters beyond server racks and developer laptops. SteamOS, the Linux-based system that runs on the Steam Deck and that Valve has increasingly pushed toward other handhelds and SteamOS on PC builds, sits on top of the same kernel. So does nearly every other Linux gaming distro, from Bazzite to Nobara.
If you're running one of those and the idea of known, unpatched, publicly documented kernel bugs makes you uneasy, the practical move right now is to check whether your distro offers a beta or testing branch and consider switching to it temporarily. Because some of the flagged fixes are already moving through beta and '-next' channels, opting into a beta update track could get you protected sooner than waiting for the next stable release to catch up.
This isn't a case of hackers actively exploiting these bugs in the wild, at least not that's been reported. It's a process failure: security reports that should have stayed quiet until fixes shipped instead became public reading material. Kroah-Hartman's quick response suggests the kernel team is treating it seriously, but until patches land on stable branches, the exposure stays open.
No timeline has been given for when fixes will reach mainline kernel releases, and neither Trend Micro's Zero Day Initiative nor the kernel security team has published a full account of how the reports ended up public. Anyone running a Linux gaming rig should keep an eye on their distro's update channel over the coming days.
CDFiled by The Computing Desk
Laptops, desktops, processors, graphics cards and the operating systems that run on them.
More from this desk →
Be the first to comment
Join the argument. No password, just your email or a passkey.